vCISO for Semiconductor and Electronics Manufacturers

Your company has cybersecurity obligations it can't ignore and no one on staff whose job it is to own them. That's the gap a vCISO fills.

A virtual CISO (vCISO) for electronics manufacturers provides executive-level cybersecurity leadership on a fractional basis, giving mid-market companies access to the strategic direction, risk management, and compliance governance that a full-time CISO delivers, without the $200K-$350K annual salary that comes with hiring one. That definition covers the basics. Here's what it looks like in an electronics manufacturing company.

The Scenario Most Electronics Manufacturers Are Living In

Your company has 150 employees. You make PCBs for defense and commercial customers. You have 2 IT people.

Last quarter, your largest OEM customer sent a vendor security questionnaire. Your IT admin spent 3 weeks filling it out, mostly guessing. The answers were incomplete. Several questions about governance, risk management, and incident response plans had no good answers because nobody owns those programs.

This quarter, your CMMC assessment is on the calendar. Your IT team has been implementing NIST SP 800-171 controls, but there's no documented risk register, no formal security policies, and no one coordinating with the assessor. Your CEO asks your IT admin when you'll be ready. The honest answer is "I don't know."

A production machine went down last month because of a firmware update conflict. It turned out the vendor had remote access to the system through an undocumented VPN connection. Nobody knew it existed until it caused a problem. There's no vendor access policy. No access review process. No one whose job it is to manage these things.

Your company doesn't need a $300K CISO. It needs the function. Governance. Risk oversight. Compliance program management. Assessor coordination. Security strategy. A vCISO delivers that function at a fraction of the cost.
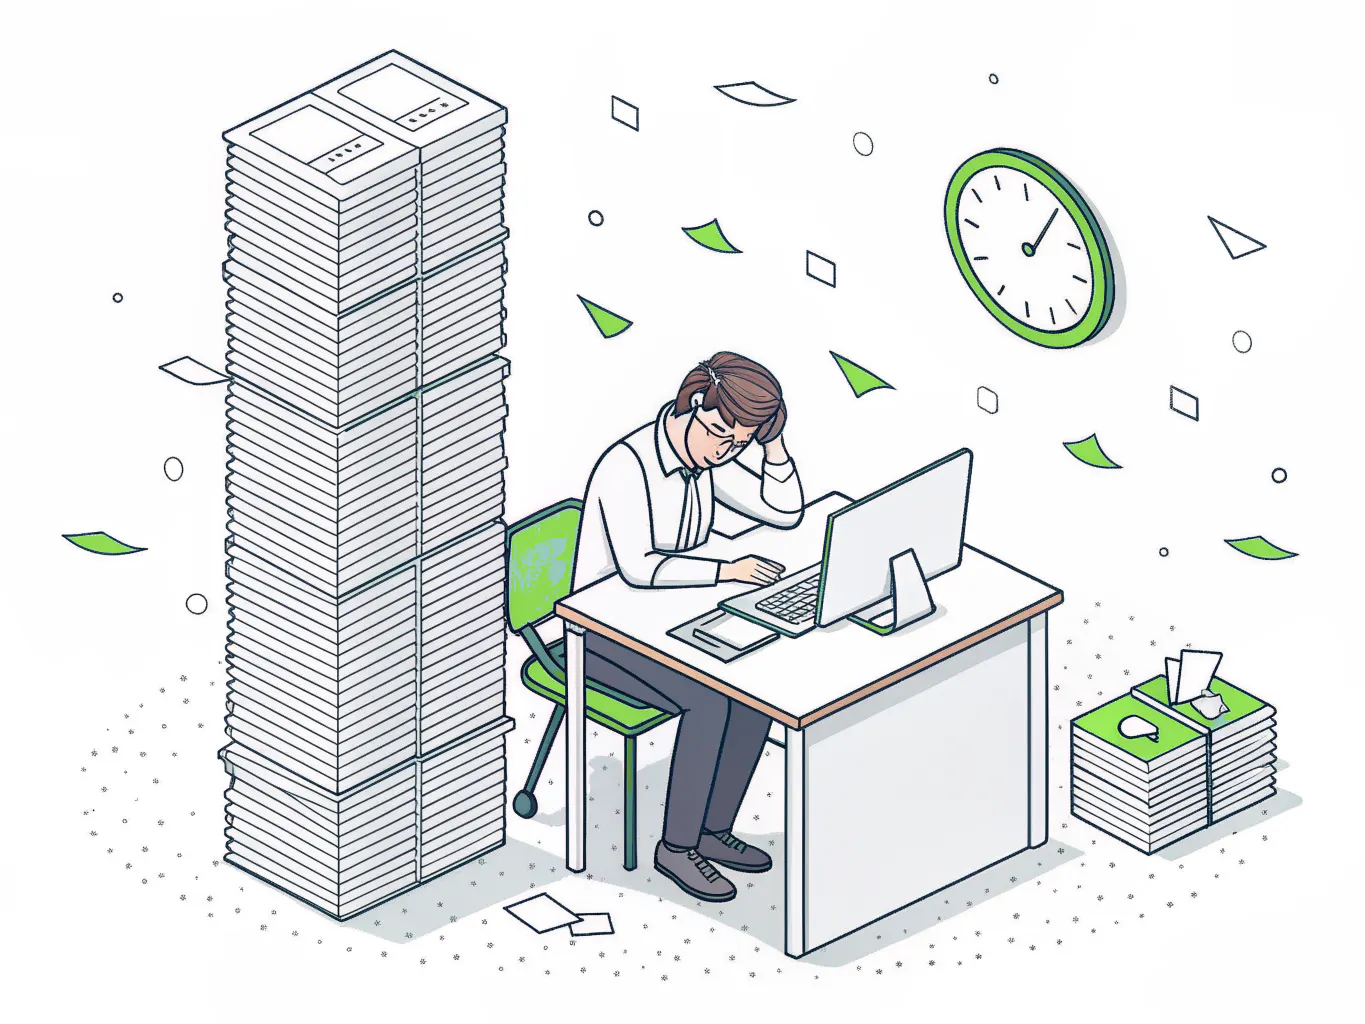
Line illustration of a single IT worker at a desk beside a tall stack of paperwork, a circuit board and a clock

What a vCISO Actually Does for an Electronics Manufacturer

A vCISO isn't a consultant who drops a report and disappears. It's an ongoing leadership role, typically scoped at 10-20 hours per month, with defined responsibilities.

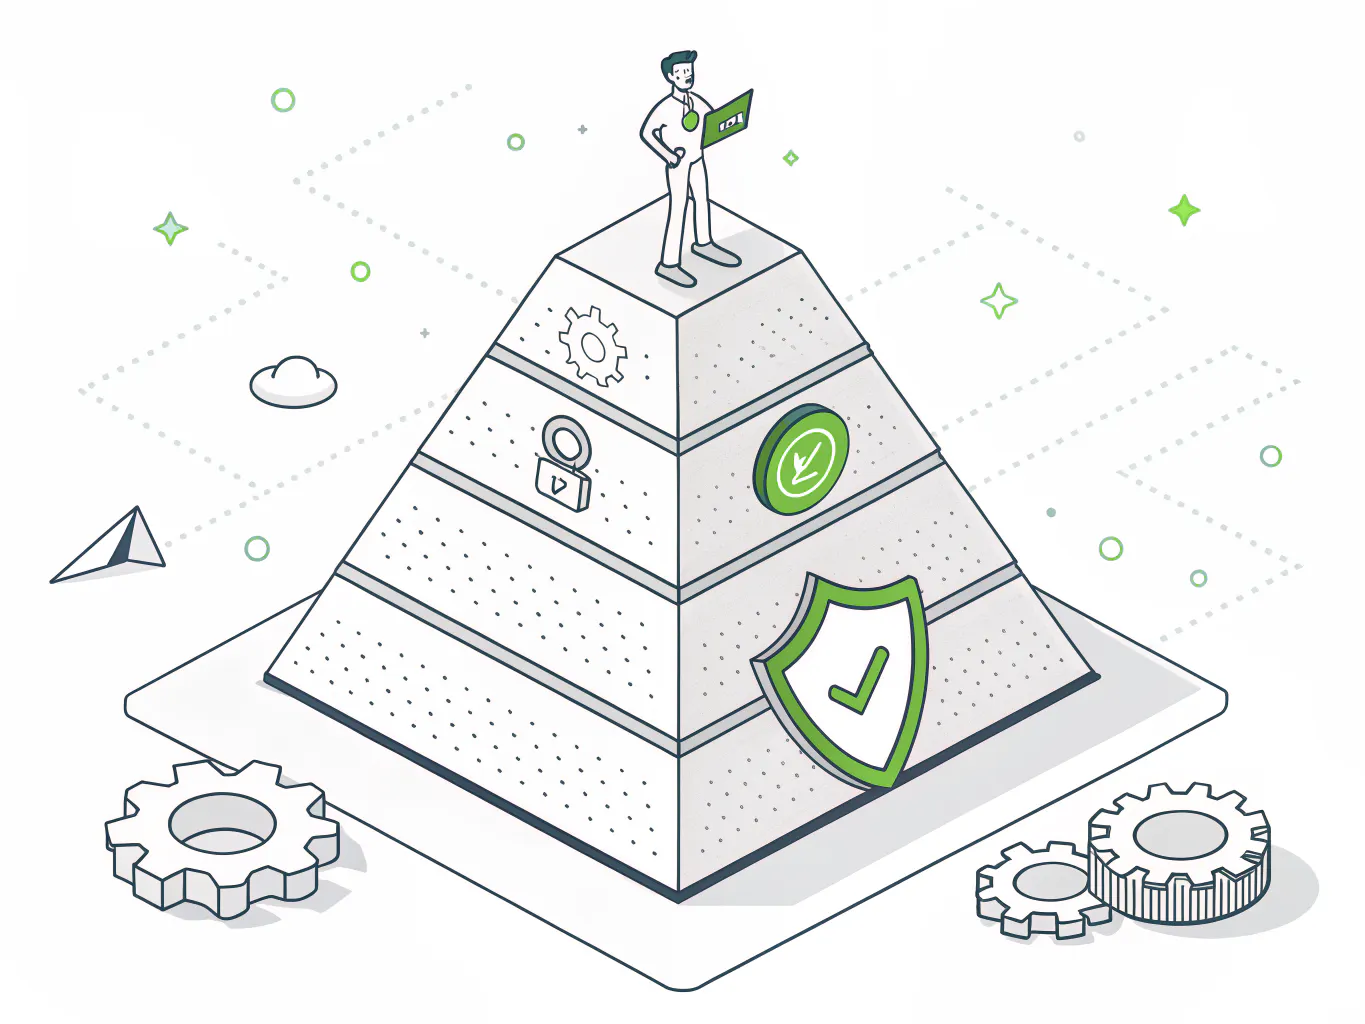
Line illustration of a three-tier layered pyramid with a leader figure on top, a shield in the middle and a gear at the base

vCISO vs. Full-Time CISO: What Changes and What Doesn't

vCISO Full-Time CISO
Annual cost$50K-$150K (typical for 10-20 hrs/month)$200K-$350K+ salary + benefits
AvailabilityScheduled + on-call for incidentsFull-time
Breadth of experienceMultiple industries and environmentsDeep single-company context
Hiring timelineWeeksMonths (senior security leadership is hard to recruit)
ScalabilityAdjust hours as needs changeFixed headcount
Cross-industry threat intelligenceYes (sees patterns across clients)Limited to internal view

For a 100-500 seat electronics manufacturer, a full-time CISO is rarely justifiable. The work is real, but it's not 40 hours a week of work. It's 10-20 hours a month of strategic leadership layered on top of the execution your IT team and managed security provider handle.

The vCISO provides what an average cost savings of 30-40% compared to a full-time hire, according to industry benchmarks. But the real value isn't the savings. It's getting the function at all. Right now, most mid-market electronics manufacturers have nobody in this role. That's the actual problem.

How It Works With Your IT Team and Your Managed Security Provider

The vCISO doesn't do the technical work. That's not the point.

Your IT team handles day-to-day operations. Your managed security provider (Consilien's IC24 Managed Cybersecurity) runs 24/7 monitoring, endpoint protection, vulnerability management, and incident response. Your vCISO sits above both, providing strategic direction.

The vCISO tells your IT team and security provider what to prioritize. They own the roadmap. They make sure the security program serves the business, not just the technology. They're the person your CEO calls when a customer asks about your security posture. They're the person who coordinates with the CMMC assessor. They're the person who reviews the risk register and says "this is our biggest exposure, fix it this quarter."

That's how the layers work. Execution (IT team + managed security). Strategy and governance (vCISO). Business decisions (your leadership).

What Triggers the Need for a vCISO

Companies don't wake up one morning and decide they need a vCISO. Something triggers it.

A customer sends a security questionnaire nobody can answer.

The SSCA, an OEM vendor security assessment, or a cyber insurance renewal form. The IT admin does their best. The gaps are obvious. Leadership realizes nobody owns this.

A compliance deadline arrives.

CMMC assessment on the calendar. ISO 27001 certification required by a new customer. ITAR compliance questions from a prime contractor. The technical controls might be partly in place. The governance, documentation, and assessor coordination aren't.

An incident happens.

A ransomware near-miss. A phishing attack that almost succeeded. A vendor access issue that exposed production systems. Leadership asks "how do we make sure this doesn't happen again?" and there's no one with the authority and expertise to answer.

Cyber insurance renewal gets complicated.

The underwriter asks for an incident response plan, evidence of security monitoring, and a named person responsible for cybersecurity. You don't have any of those things documented.

What Electronics Manufacturers Ask About vCISO Services

How many hours per month does a vCISO spend with us?


Typically 10-20 hours per month for a mid-market electronics manufacturer. More during initial program build-out, compliance assessments, or incident response. Less once the program is mature and running.

The Cost of Not Having This Function

Electronics manufacturers without a vCISO typically experience these outcomes.

Compliance programs stall after the initial assessment. Nobody drives remediation forward.

Security questionnaires take weeks to complete and produce incomplete answers. Customer trust erodes.

Incidents don't have a coordinated response. Recovery takes longer. Documentation is missing. Post-incident reporting is chaotic.

Insurance renewals get harder and more expensive. Underwriters see the gaps.

Leadership lacks visibility into IT risk. Decisions get made without understanding the actual exposure.

A vCISO costs a fraction of a full-time hire and eliminates all of these patterns.

Consilien's vCISO services are built into our engagement model for electronics manufacturers. Your vCISO works alongside your IT team and our managed security operation. Strategy, governance, compliance, risk management, and executive communication. All covered.

Our Clients' Success

25+ years managing IT for manufacturers. MSP 501 for 2025 and 2026. Highly rated on Clutch.

Explore the full IT services hub for semiconductor and electronics manufacturers or read about compliance readiness and managed cybersecurity for this vertical.